



ISO 27001 Information Security Management Systems
Protect your information. Strengthen trust. Reduce risk.
Information is one of an organisation's most valuable assets. Whether it includes customer data, financial records, intellectual property, employee information, or commercially sensitive business information, protecting that information is essential to maintaining trust, ensuring compliance, and supporting business success.
ISO/IEC 27001 is the internationally recognised standard for Information Security Management Systems (ISMS). It provides a structured framework for identifying, managing, and reducing information security risks while safeguarding the confidentiality, integrity, and availability of information.
As organisations become increasingly reliant on digital systems and data-driven operations, the threats posed by cyber incidents, data breaches, and unauthorised access continue to grow. ISO 27001 helps organisations proactively manage these risks through a systematic and risk-based approach to information security.
Implementing an ISO 27001 certified Information Security Management System can help your organisation:
- Protect sensitive information and critical business assets
- Reduce the risk of cyber security incidents and data breaches
- Meet regulatory, legal, and contractual obligations
- Strengthen customer and stakeholder confidence
- Improve governance and risk management practices
- Demonstrate a commitment to information security best practice
- Support business resilience and operational continuity
- Drive continual improvement in security processes and controls
Internationally Recognised Information Security Best Practice
ISO 27001 sets out the requirements for establishing, implementing, maintaining, monitoring, and continually improving an Information Security Management System. Certification provides independent assurance that your organisation has implemented internationally recognised controls and processes to manage information security risks effectively.
Achieving certification demonstrates to customers, regulators, partners, and stakeholders that information security is a strategic priority and that your organisation is committed to protecting the information entrusted to it.
Supported by ISO/IEC 27002
ISO 27001 is supported by ISO/IEC 27002, which provides detailed guidance on information security controls and best practices. Together, these standards offer a comprehensive framework for establishing effective governance, security controls, and risk management processes across the organisation.
Achieve ISO 27001 certification with confidence and demonstrate your organisation's commitment to information security, risk management, and internationally recognised best practice.
Why choose Telarc?
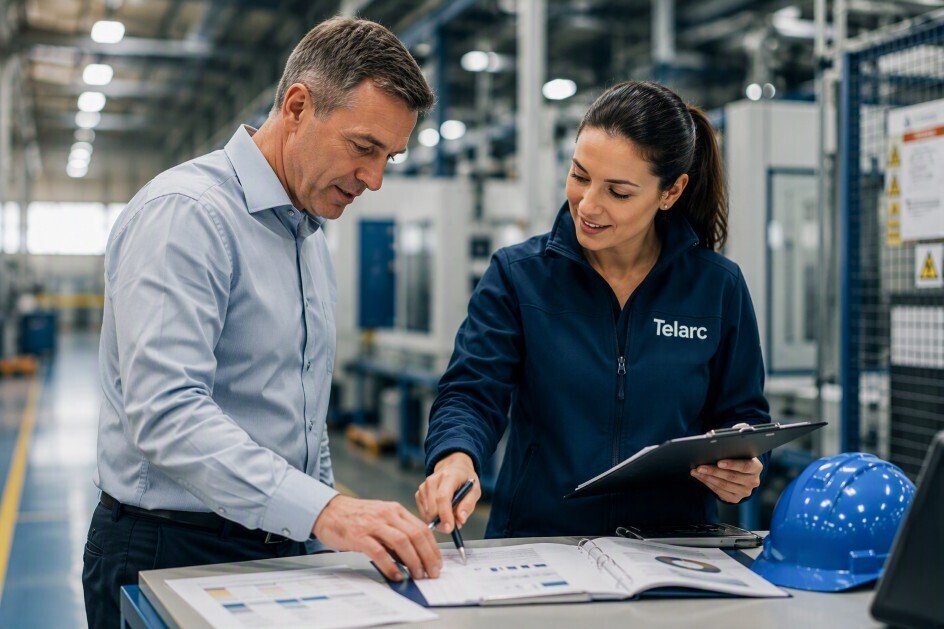
For more than 50 years, Telarc has been providing independent certification and assurance services to organisations across New Zealand and beyond. As a Crown-owned certification body, we deliver credible, impartial, and professional certification services that help organisations build trust, strengthen governance, and demonstrate excellence.
Our experienced auditors understand the evolving information security landscape and take a practical, risk-based approach to certification. We work with organisations of all sizes and sectors to ensure certification is both meaningful and valuable, helping clients improve security performance while meeting stakeholder expectations.
Achieve certification with confidence
Telarc's experienced team will guide you through the ISO 27001 certification process with professionalism, transparency, and technical expertise. Our goal is to make certification a valuable business improvement journey that strengthens information security, protects organisational assets, and builds confidence among customers and stakeholders.
The experience was excellent and surpassed the experience we have had with anyone else that we have engaged with to date on our ISO journey.
Related News

New MPI Food Import Rules Take Effect in 2027
Read More

ISO 9001:2026 & ISO 14001:2026 Are Coming
Read More

FSSC 22000 Version 7 Update
Read More